Report Type | Subject Alleged 22 TB data theft from Indian diplomatic and foreign-affairs entities (Indian Embassies and Ministry of Foreign Affairs) | Incident Date 23 September 2026 (forum post) |
Report Date 28 September 2026 | Threat Actor Handle RAYLEAS (X Forums) | Telegram: @Rayhucker | Attributed Identity (OSINT) Rayyan Afridi, Pakistan-based (Peshawar, Khyber Pakhtunkhwa); founder of AsefaSec |
1. Executive Summary
On 23rd September 2026, a threat actor on an underground forum named X Forums1 is reportedly claiming approximately 22 TB of data allegedly stolen from Indian diplomatic and foreign-affairs entities, including the Indian Embassy and Ministry of Foreign Affairs, for US$200,000. The accompanying material shown in the sample pictures references a substantial collection of official documents and large reference databases, including senior appointment circulars, Foreign Service Board records, IFS officer language-proficiency lists, organizational charts, officer directories, journal databases, Foreign Service Institute resources, telephone directories, and large government reference datasets.
2. Leak Sample Evidence
Sample material published by the actor alongside the sale offer is reproduced below.
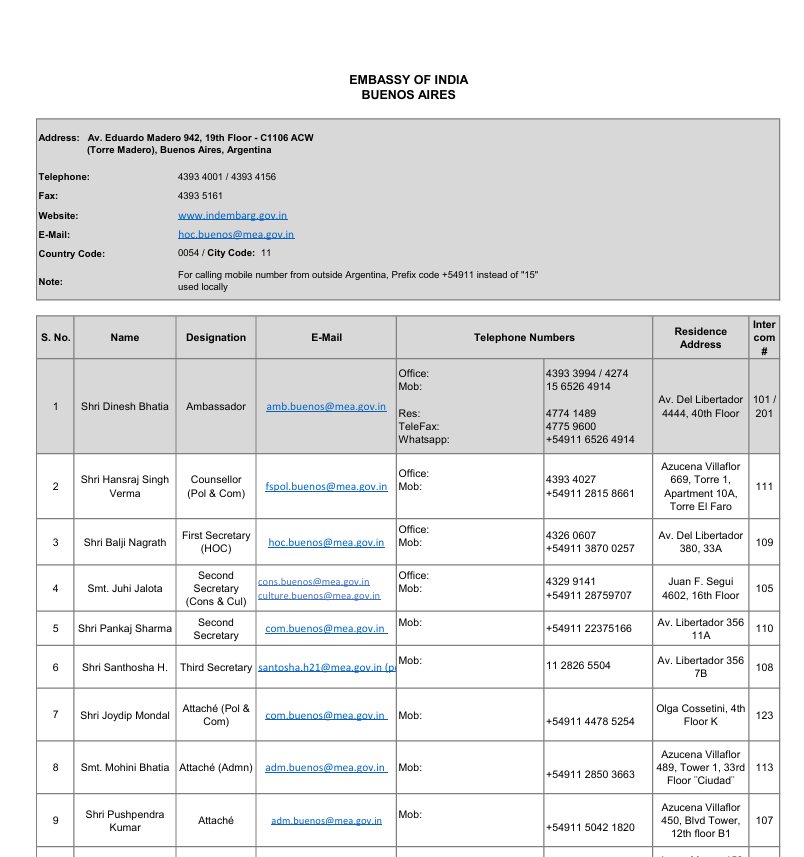
Figure 1: Sample document from the leak: Embassy of India, Buenos Aires — officer directory with designations, e-mail addresses and telephone numbers.

Figure 2: Forum sale post header: “FULL INDIAN EMBASSIES BREACHED TOTAL OF 22TB DATA” (Indian Division Directories).
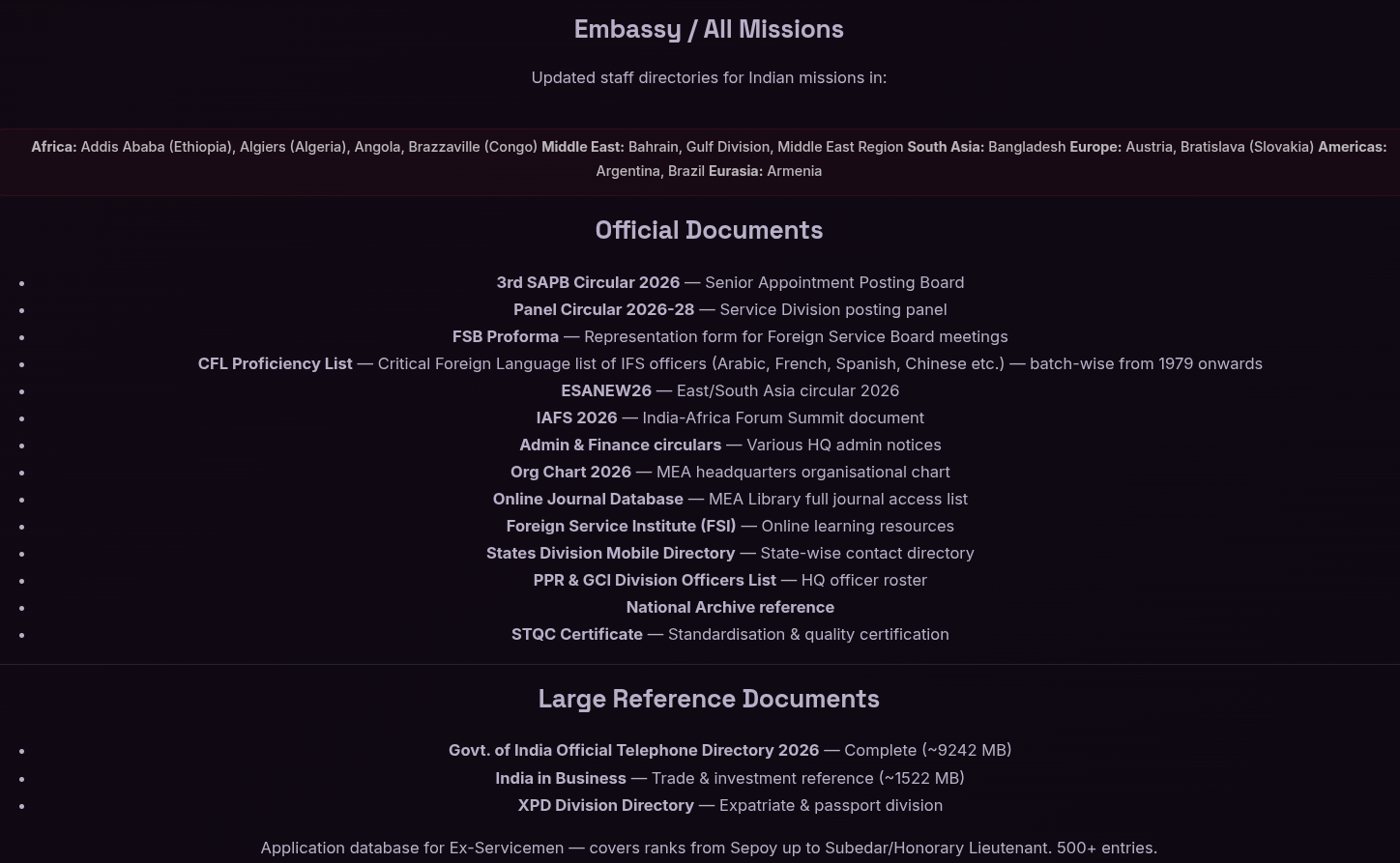
Figure 3: Sample listing: Embassy / All Missions directories, official documents and large reference documents.

Figure 4: Sample listing: Indian HQ Division Directories — MEA headquarters divisions covered.
3. Key Incident Points
The threat actor is operating under the handle “RAYLEAS” shows Moderator (as per his profile on X Forums) and joined the forum on 24th June 2025 and currently has 10 messages and a reaction score of 2.
The actor has also shared the Telegram handle “@Rayhucker” and a session ID (
056ab8b053a3b77bf0bab81ab3c15be6a360360f13c1251328780f3d0e23355d4d) for sample access and potential data purchase inquiries.The threat actor’s feed contains multiple data-selling posts allegedly related to Indian defence entities, including the Indian Army, BSF and NSG, as well as the Bangladesh Ministry of Defence and CIA email data allegedly associated with the Taliban.
One of the threat actor’s posts specifically states that they are seeking military-related documents from countries including India, China, Pakistan, Iran’s IRGC, Saudi Arabia, and other countries across the Middle East. This post provides an indication of the actor’s stated targets and areas of interest.
Further analysis of the sample provided by the threat actor determined that the exposed records were already present in publicly accessible open-source datasets.
4. Threat Actor Identification
The threat actor has shared the Telegram handle “@Rayhucker”, which appears to have links to the name “Rayyan Afridi” based on previously observed Historical Display name associated with the account. The Telegram account is also associated with a Pakistan-based mobile number +92 32******61 and CNIC (Computerized National Identity Card) Number 1730*-6****63-7.

Further open-source checks of the mobile number using publicly available Pakistan-focused OSINT sources indicated a possible association with an individual identified as “Romina Afridi,” reportedly mother of Rayyan Afridi located in the Peshawar, Khyber Pakhtunkhwa region of Pakistan.
4.1 About Rayyan Afridi
The threat actor Github Account2 was further identified, revealing his association with a Pakistan based company named AsefaSec (as founder of company, registered in 2025).
AsefaSec is a Cybersecurity firm focused on helping organizations identify, mitigate, and proactively defend against evolving digital threats and specialized in security services, including penetration testing, vulnerability assessments, application and API security, cloud security, red team assessments, and security consulting.
The individual has shared one Instagram story mentioning ISPR3 (Inter Service Public Relations), further confirming his association with Pakistan ISPR.
AsefaSec, a company founded by Rayyan Afridi, references capabilities involving ransomware threats, APT group identification, the release of stealth exploits, and zero-day RCE detection. These references have been cited as indicators of potential associations with dark-web and cybercriminal-related activities.
His Instagram and LinkedIn post shows GoDaddy, Skeler Security, Secure Purple, Black Byt3, Intel Forge and Singapore Police Force as Strategic partners.
Rayyan Afridi is currently working as Penetration Tester on Contract at Digiinn360 (an Islamabad based Cyber Security Firm).
The social media post of Rayyan Afridi, also shows his participation in Cyber Security Hackathons and Events.
The Threat actor Rayyan Afridi has also been observed using the alias “RAY,” derived from the first three letters of his name, across X Forums (Rayleas), Telegram (Rayhucker), GitHub (Ray0x01), and LinkedIn (Rayreal). The consistent use of this alias across these platforms further supports the assessment of a potential connection between the accounts and the identified threat actor.
4.2 Publicly Available Data Repackaged as a “Leak”
Further analysis of the sample shared by the threat actor identified substantial overlap with information already available through publicly accessible sources.
This demonstrates why dark-web leak claims should not be treated as confirmed breaches without validating the data’s provenance, uniqueness, and source. This reinforces the need for independent validation before classifying dark-web claims as genuine breaches.
Telegram groups joined by threat actor along with his messages in groups and common users in the groups were found. The detailed analysis along with screenshots are attached below for reference.
4.3 Historical Display Name
Historical Display Name | Recorded Timestamp |
|---|---|
Rayyan Afridi | 24/09/2026, 22:19:50 |
4.4 Threat Actor Profile on X Forums, Telegram and Session
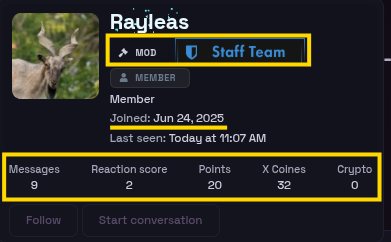 Figure 5: X Forums profile of “Rayleas” — Staff Team / MOD, joined 24 Jun 2025, 9 messages, reaction score 2. | 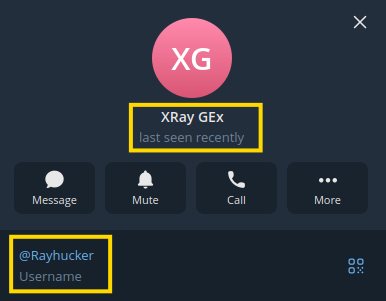 Figure 6: Telegram profile — username @Rayhucker (display name shown: “XRay GEx”). |
4.5 Telegram Groups Joined by the Threat Actor
Group / Chat Name | Chat Id | Target Message Count | Last Active Date |
|---|---|---|---|
TECTUM 🔗 Fastest Blockchain & SoftNote | 1284662604 | 2 | 1/17/2025, 8:34:58 AM |
4.6 Message of Threat Actor in Telegram Groups
Timestamp | Group Title | Message |
|---|---|---|
1/17/2025, 8:34:58 AM | TECTUM 🔗 Fastest Blockchain & SoftNote | who can i dm? and post the vulnerabilities |
1/17/2025, 8:34:43 AM | TECTUM 🔗 Fastest Blockchain & SoftNote | Hey There Developer Team I have found some issues in tectum it was a while ago I reported them to security team aswell but no reply then i reach put to Alexender CEO and he told me to reach you guys out here |
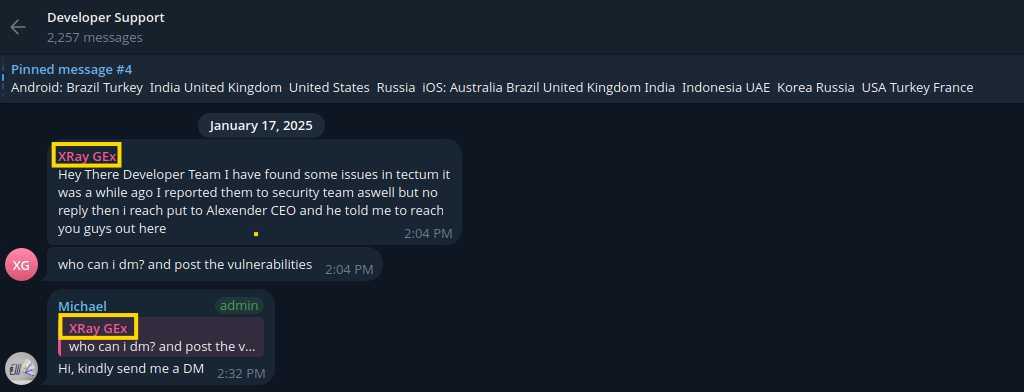
Figure 7: Telegram message screenshot (Developer Support group, January 17, 2025).
4.7 Common Users in Group
User Id | Full Name | Username | Common Group Count |
|---|---|---|---|
8815752388 | Nader | @nader4321 | 1 |
5235979983 | Ggg | @onae3725 | 1 |
7482339540 | Alex Leyendas | N/A | 1 |
7756289431 | Gal | @gostyyy | 1 |
5383071234 | NTAWUTAVUGWA Albert | @jalos23 | 1 |
7150990201 | 🅑🅘🅐🅝🅒🅞 🍥 | Web3 Incubator | @Bianco009 | 1 |
5150301439 | Dkay | @dkaysthetics | 1 |
7233664957 | Nafisa Rahman | @Netflix_Nafisa_Rohman | 1 |
1076047841 | All | @RubyboyA | 1 |
6614558869 | Jams | N/A | 1 |
5911654710 | Muhammad 🐐 | @muhammadaltamash5030 | 1 |
1830660820 | Usman Fahmiazi | @amiewww | 1 |
1250252929 | Dragon | @Poppy_Haunam | 1 |
7671238514 | Mariam Mohammed | @ariaohamm | 1 |
8067109335 | ThorSpeed 🏁 | @Thor_rose0 | 1 |
638548784 | Lung Thang | N/A | 1 |
2001392869 | FaisalWeb3 | @Daniewar | 1 |
7808400198 | Lena🥰 | N/A | 1 |
7318213074 | jiayin | N/A | 1 |
7793042041 | John Staz | N/A | 1 |
6854949519 | Ayesha Maher | @Ayeshamaher | 1 |
2101775908 | Pradayrol Cel | @Invest_cel | 1 |
5667286076 | PAVEL [ Owner - Crypto Analysis ] | @Owner_analysis | 1 |
5452721617 | Mirko | @Cviki89 | 1 |
6308997782 | FADAFADAWEB3 | @Fadafadaweb3 | 1 |
5417197005 | Anderson | @Andi1731 | 1 |
6594922232 | Zuma𝕏 | @ZumaniaX | 1 |
584653250 | Bright Swan | @Octavn | 1 |
725496190 | BrainBox | @BrainBox1212 | 1 |
5073555464 | 0xgimic | @Arrienugroho | 1 |
930064575 | Un Salida | @UnSalida | 1 |
6977647427 | Macdonald 🍅 🐾 🐐 Ekworo | @mcekworo1972 | 1 |
8360390227 | Jaelynn | Listing | @Jaelynn_OG | 1 |
6054880385 | KinGKinG | N/A | 1 |
6241313848 | Carlo FRGST-Froggies | @CarloGreatfrog | 1 |
6787713705 | Jules@margcoinOG | N/A | 1 |
983092572 | Appzz Zz ▪️ 🐾 | @PKAppz | 1 |
7857060564 | Chloe Cook | N/A | 1 |
6190388285 | Gemstone 💎 | @Gemboxes | 1 |
716078334 | Mr Dou | @Dou007 | 1 |
8487750782 | Gabriela Blofin | @Gabriela_Blofinlistings1 | 1 |
424350965 | Fat Cat | @SuicidalBear | 1 |
1055049258 | BitVogel | @stefanbaer1979 | 1 |
6232725054 | Dennie | @Dennie0313 | 1 |
6774392744 | 😉😉😉 | N/A | 1 |
7128787606 | Ivanoff | @Agent022022 | 1 |
7216038852 | Tuğçe Kılıç | N/A | 1 |
8430854234 | A.M.X | N/A | 1 |
1613275485 | vansStrong always eligible | @hiraaaaaaaa | 1 |
7172224768 | Salomeh | N/A | 1 |
4.8 Other Data Leaks Posted by Threat Actor4

Figure 8: Threads posted by the actor on X Forums (data-sale and request posts).
Date | Target | Data Size | Sample |
|---|---|---|---|
23 September 2026 | FULL INDIAN EMBASSIES + MOFA BREACHED | 22 TB | Yes |
07 September 2026 | BSF, NSG Military Movement 2026 to 2028 All Movement Deployment Etc. | 20 TB | Yes |
01 September 2026 | Ministry Of Defense All Military Colonels Data For Sale. | - | Yes |
27 August 2026 | SECRET CIA US EMAIL TO TALIBAN 08/25/2026 | 6 Pages | Yes |
21 August 2026 | Any Military Documents 2026 - India, China, Pakistan, IRGC (IRAN), Saudi Arabia, Middle East ETC. | - | - |
5. Rayyan Afridi Portfolio
Personal portfolio site attributed to the individual: https://github.com/Ray0x01/portfolio/blob/main/index.html5

Figure 9: Portfolio website — landing page (“Rayyan Afridi — Founding AsefaSec | Red Teamer | Content Creator”).

Figure 10: Portfolio website — “Classified Intel” section.

Figure 11: Portfolio website — “Mission Log” timeline.

Figure 12: Portfolio website — “Secure Channel” contact section.
5.1 Pictures of Rayyan Afridi
 Figure 13: Photograph of Rayyan Afridi. |  Figure 14: Graphic: “100 Student Leaders of Pakistan” — Rayyan Afridi, Cybersecurity Professional & Founder AsefaSec. |
5.2 Identified Accounts of Rayyan Afridi
Github | |
|---|---|
YouTube |

Figure 15: GitHub profile — “Hello, I’m Rayyan Afridi” (Ray0x01), Peshawar, Pakistan.

Figure 16: Instagram profile — ryan.povz, “Founder @asefasec”, story highlights including ISPR and ECP.

Figure 17: LinkedIn profile — Rayyan (Ray) Afridi, Offensive Security Specialist, Islamabad, Pakistan (Digiinn360).

Figure 18: YouTube channel — “Rayyan Afridi ~ Pentester”.
6. About AsefaSec
AsefaSec6 is a Cybersecurity firm focused on helping organizations identify, mitigate, and proactively defend against evolving digital threats and specialized in security services, including penetration testing, vulnerability assessments, application and API security, cloud security, red team assessments, and security consulting.
Company LinkedIn: https://www.linkedin.com/company/asefasec/
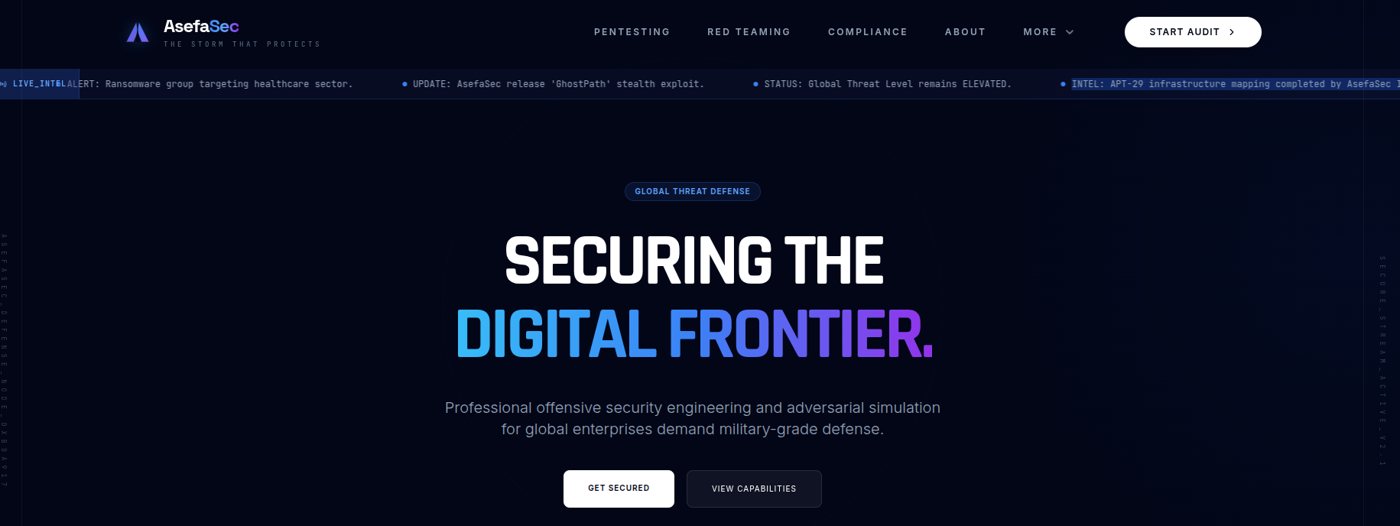
Figure 19: AsefaSec website — “Securing the Digital Frontier”.

Figure 20: AsefaSec website — “Global Capabilities” (red teaming, web & API pentest, cloud security, code review).

Figure 21: AsefaSec team-update graphic.

Figure 22: AsefaSec team-update graphic.

Figure 23: AsefaSec team-update graphic.

Figure 24: AsefaSec LinkedIn company page.

Figure 25: AsefaSec LinkedIn overview — core focus areas and company details.
7. Social Media Posts of ISPR Connection and Participation in Hackathons and Events
A7
https://www.instagram.com/stories/highlights/17909603175299548/

Figure 26: Instagram story A — highlighted “ISPR” and “Pak Cyber Warrior” items.
B8
https://www.instagram.com/stories/highlights/17868677184417614/

Figure 27: Instagram story B — event participation.
C9
https://www.instagram.com/stories/highlights/17991319349728389/

Figure 28: Instagram story C — workshop at National Skills University Islamabad featuring AsefaSec.
D10
https://www.instagram.com/stories/highlights/17991319349728389/

Figure 29: Instagram story D — event / award ceremony.
8. Threat Actor Indicators Summary
Consolidated from the data above for tracking and monitoring purposes.
Indicator Type | Value | Context |
|---|---|---|
Forum handle | RAYLEAS (X Forums) | Moderator/Staff Team; joined 24 Jun 2025 |
Forum thread | https://xforums.st/threads/india-full-indian-embassies-mofa-breached-total-of-22tb-data.701718/ | Sale post, 22 TB, US$200,000 |
Telegram | @Rayhucker | Contact for samples and purchase |
Telegram historical display name | Rayyan Afridi | Recorded 24/09/2026, 22:19:50 |
Session ID |
| Contact for samples and purchase |
Mobile number | +92 32******61 | Pakistan-based; linked to Telegram account |
CNIC | 1730*-6****63-7 | Linked to Telegram account |
GitHub | Personal profile | |
Personal profile | ||
Personal profile | ||
YouTube | Personal channel | |
Company website | AsefaSec (founded 2025) | |
Company LinkedIn | AsefaSec |
9. Analyst Notes and Recommended Actions
Analyst notes. The data volume (22 TB), price and breach claims are statements made by the actor; the sample material appears consistent with diplomatic contact directories and administrative circulars, but full authenticity and scope are not independently confirmed. Identity attribution rests on open-source correlation (display-name history, linked social and code-hosting accounts, and Pakistan-based number/CNIC linkage) and should be treated as an intelligence assessment, not a legal finding. The ISPR-related Instagram story is an associative indicator.
Recommended actions.
Validate the sample material against internal records to confirm authenticity and identify the affected missions and divisions.
Monitor the X Forums thread, the Telegram handle @Rayhucker and the Session ID for new sample releases or sales.
Warn diplomatic and MEA staff about targeted phishing and impersonation attempts that could abuse leaked officer directories and contact details.
Review access controls and credentials for systems holding directory, circular and reference-database content.
Footnotes
https://xforums.st/threads/india-full-indian-embassies-mofa-breached-total-of-22tb-data.701718/ ↩
ISPR is the media and public relations wing of the Pakistan Armed Forces ↩
https://xforums.st/search/1087489/?c[users]=Rayleas&o=date ↩
https://www.instagram.com/stories/highlights/17909603175299548/ ↩
https://www.instagram.com/stories/highlights/17868677184417614/ ↩
https://www.instagram.com/stories/highlights/17991319349728389/ ↩
https://www.instagram.com/stories/highlights/17991319349728389/ ↩